% This ZIP makes heavy use of mathematical markup. If you can see this, you may want to instead view the rendered version at https://zips.z.cash/zip-0032 .
Terminology
The key words "MUST", "MUST NOT", "SHOULD", "SHOULD NOT", and "MAY" in this document are to be interpreted as described in RFC 2119. [1]
"Jubjub" refers to the elliptic curve defined in [16].
A "chain code" is a cryptovalue that is needed, in addition to a spending key, in order to derive descendant keys and addresses of that key.
The terms "Testnet" and "Mainnet" are to be interpreted as described in section 3.12 of the Zcash Protocol Specification [10].
Abstract
This proposal defines a mechanism for extending hierarchical deterministic wallets, as decribed in BIP 32 [2], to support Zcash's shielded addresses.
The initial parts of the specification define (mostly) equivalent, but independent, systems for deriving a tree of key components from a single seed, for the following shielded pools (which have different internal key structures):
Sapling
Orchard
Previous versions of this document also defined a similar derivation system for the Sprout shielded pool. This has been removed since it was never used, and is unlikely to be used given that zcashd no longer generates Sprout addresses (and neither Zebra nor the mobile SDKs have ever done so).
The last part shows how to use these trees in the context of existing BIP 44 [5] wallets.
This specification complements the existing use by some Zcash wallets of BIP 32 and BIP 44 for transparent Zcash addresses, and is not intended to deprecate that usage (privacy risks of using transparent addresses notwithstanding).
Motivation
BIP 32 [2] is the standard mechanism by which wallets for Bitcoin and its derivatives (including Zcash's transparent addresses [6]) generate keys and addresses deterministically. This has several advantages over random generation:
Wallets only need to store a single seed (particularly useful for hardware wallets).
A one-time backup of the seed (usually stored as a word phrase [3]) can be used to recover funds from all future addresses.
Keys are arranged into a tree of chains, enabling wallets to represent "accounts" or other high-level structures.
Viewing authority or spending authority can be delegated independently for sub-trees without compromising the master seed.
At present, no such equivalent exists for Zcash's shielded addresses. This is of particular concern for hardware wallets; all currently-marketed devices only store a seed internally, and have trained their users to only backup that seed. Given that the Sapling upgrade will make it feasible to use hardware wallets with shielded addresses, it is desirable to have a standard mechanism for deriving them.
Conventions
Most of the notation and functions used in this ZIP are defined in the Zcash protocol specification [9]. They are reproduced here for convenience:
means the sequence formed from the first elements of .
means the concatenation of sequences then .
means scalar multiplication of the elliptic curve point by the scalar .
is the integer in range represented in little-endian order by the byte sequence of length .
is the sequence of bits representing in little-endian order.
is defined as follows when is a multiple of : convert each group of 8 bits in to a byte value with the least significant bit first, and concatenate the resulting bytes in the same order as the groups.
is the representation of the Jubjub elliptic curve point as a bit sequence, defined in [16].
refers to unkeyed BLAKE2b-256 in sequential mode, with an output digest length of 32 bytes, 16-byte personalization string , and input .
refers to unkeyed BLAKE2b-512 in sequential mode, with an output digest length of 64 bytes, 16-byte personalization string , and input .
\mathsf{BLAKE2b}\text{-}\mathsf{512}(\texttt{“Zcash_ExpandSeed”},
is the order of the Jubjub large prime subgroup.
is the order of the Pallas curve.
.
.
maps a diversifier to a base point on the Jubjub elliptic curve, or to if the diversifier is invalid. It is instantiated in [14].
The following algorithm standardized in [23] is used:
refers to the FF1 encryption algorithm using AES with a 256-bit , and parameters . It will be used only with the empty string \texttt{“”} as the . is a sequence of 88 bits, as is the output.
We also define the following conversion function:
is the byte sequence of length representing in little-endian order the integer in range . It is the reverse operation of .
Implementors should note that this ZIP is consistently little-endian (in keeping with the Sapling and Orchard specifications), which is the opposite of BIP 32.
We adapt the path notation of BIP 32 [2] to describe shielded HD paths, using prime marks () to indicate hardened derivation () as in BIP 44 [5]:
is written as .
Specification: Sapling key derivation
Sapling extended keys
BIP 32 defines a method to derive a number of child keys from a parent key. In order to prevent these from depending solely on the parent key itself, both the private and public keys are extended with a 32-byte chain code. We similarly extend Sapling keys with a chain code here. However, the concepts of "private" and "public" keys in BIP 32 do not map cleanly to Sapling's key components. We take the following approach:
We derive child Sapling expanded spending keys, rather than Sapling spending keys. This enables us to implement both hardened and non-hardened derivation modes (the latter being incompatible with Sapling spending keys).
We do not derive Sapling public keys directly, as this would prevent the use of diversified addresses. Instead, we derive Sapling full viewing keys, from which payment addresses can be generated. This maintains the trust semantics of BIP 32: someone with access to a BIP 32 extended public key is able to view all transactions involving that address, which a Sapling full viewing key also enables.
We represent a Sapling extended spending key as , where is the normal Sapling expanded spending key, is a diversifier key, and is the chain code.
We represent a Sapling extended full viewing key as , where is the normal Sapling full viewing key, is the same diversifier key as above, and is the chain code.
Sapling helper functions
Define
Sapling master key generation
Let be a seed byte sequence of a chosen length, which MUST be at least 32 and at most 252 bytes.
Calculate I = \mathsf{BLAKE2b}\text{-}\mathsf{512}(\texttt{“ZcashIP32Sapling”}, S).
Split into two 32-byte sequences, and .
Use as the master spending key , and as the master chain code .
Calculate , , and via the standard Sapling derivation [11]:
\mathsf{ask}_m = \mathsf{ToScalar^{Sapling}}(\mathsf{PRF^{expand}}(\mathsf{sk}_m, [\texttt{0x00}]))
\mathsf{nsk}_m = \mathsf{ToScalar^{Sapling}}(\mathsf{PRF^{expand}}(\mathsf{sk}_m, [\texttt{0x01}]))
\mathsf{ovk}_m = \mathsf{truncate}_{32}(\mathsf{PRF^{expand}}(\mathsf{sk}_m, [\texttt{0x02}])).
Calculate similarly:
\mathsf{dk}_m = \mathsf{truncate}_{32}(\mathsf{PRF^{expand}}(\mathsf{sk}_m, [\texttt{0x10}])).
Return as the master extended spending key .
Note that the master extended key is invalid if is , or if the corresponding derived as specified in [11] is .
Sapling child key derivation
As in BIP 32, the method for deriving a child extended key, given a parent extended key and an index , depends on the type of key being derived, and whether this is a hardened or non-hardened derivation.
Deriving a child extended spending key
Check whether (whether the child is a hardened key).
If so (hardened child): let I = \mathsf{PRF^{expand}}(\mathsf{c}_{par}, [\texttt{0x11}].
If not (normal child): let I = \mathsf{PRF^{expand}}(\mathsf{c}_{par}, [\texttt{0x12}] where is the full viewing key derived from as described in [11].
Split into two 32-byte sequences, and .
Let I_\mathsf{ask} = \mathsf{ToScalar^{Sapling}}(\mathsf{PRF^{expand}}(I_L, [\texttt{0x13}])).
Let I_\mathsf{nsk} = \mathsf{ToScalar^{Sapling}}(\mathsf{PRF^{expand}}(I_L, [\texttt{0x14}])).
Return:
\mathsf{ovk}_i = \mathsf{truncate}_{32}(\mathsf{PRF^{expand}}(I_L, [\texttt{0x15}]
\mathsf{dk}_i = \mathsf{truncate}_{32}(\mathsf{PRF^{expand}}(I_L, [\texttt{0x16}]
.
Note that the child extended key is invalid if is , or if the corresponding derived as specified in [11] is .
Deriving a child extended full viewing key
Let be as defined in [15] and let be as defined in [11].
Check whether (whether the child is a hardened key).
If so (hardened child): return failure.
If not (normal child): let I = \mathsf{PRF^{expand}}(\mathsf{c}_{par}, [\texttt{0x12}].
Split into two 32-byte sequences, and .
Let I_\mathsf{ask} = \mathsf{ToScalar^{Sapling}}(\mathsf{PRF^{expand}}(I_L, [\texttt{0x13}])).
Let I_\mathsf{nsk} = \mathsf{ToScalar^{Sapling}}(\mathsf{PRF^{expand}}(I_L, [\texttt{0x14}])).
Return:
\mathsf{ovk}_i = \mathsf{truncate}_{32}(\mathsf{PRF^{expand}}(I_L, [\texttt{0x15}]
\mathsf{dk}_i = \mathsf{truncate}_{32}(\mathsf{PRF^{expand}}(I_L, [\texttt{0x16}]
.
Note that the child extended key is invalid if is the zero point of Jubjub, or if the corresponding derived as specified in [11] is .
Sapling internal key derivation
The above derivation mechanisms produce external addresses suitable for giving out to senders. We also want to be able to produce another address derived from a given external address, for use by wallets for internal operations such as change and auto-shielding. Unlike BIP 44 that allows deriving a stream of external and internal addresses in the same hierarchical derivation tree [5], for any external full viewing key we only need to be able to derive a single internal full viewing key that has viewing authority for just internal transfers. We also need to be able to derive the corresponding internal spending key if we have the external spending key.
Deriving a Sapling internal spending key
Let be the external spending key.
Derive the corresponding and as specified in [11].
Let I = \textsf{BLAKE2b-256}(\texttt{"Zcash_SaplingInt"}, \mathsf{EncodeExtFVKParts}(\mathsf{ak}, \mathsf{nk}, \mathsf{ovk}, \mathsf{dk})).
Let .
Let .
Let .
Split into two 32-byte sequences, and .
Return the internal spending key as .
Note that the child extended key is invalid if is the zero point of Jubjub, or if the corresponding derived as specified in [11] is .
Deriving a Sapling internal full viewing key
Let be as defined in [11].
Let be the external full viewing key.
Let I = \textsf{BLAKE2b-256}(\texttt{"Zcash_SaplingInt"}, \mathsf{EncodeExtFVKParts}(\mathsf{ak}, \mathsf{nk}, \mathsf{ovk}, \mathsf{dk})).
Let .
Let .
Let .
Split into two 32-byte sequences, and .
Return the internal full viewing key as .
This design uses the same technique as non-hardened derivation to obtain a full viewing key with the same spend authority (the private key corresponding to ) as the original, but viewing authority only for internal transfers.
The values of , , and are the same between deriving a full viewing key, and deriving the corresponding spending key. Both of these derivations are shown in the following diagram:
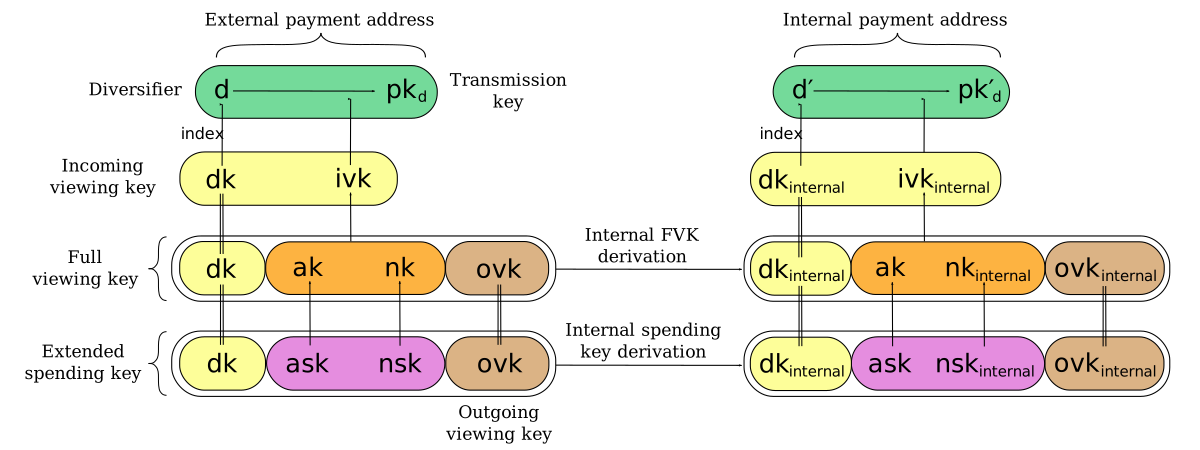
Diagram of Sapling internal key derivation
(For simplicity, the proof authorizing key is not shown.)
This method of deriving internal keys is applied to external keys that are children of the Account level. It was implemented in zcashd as part of support for ZIP 316 [8].
Note that the internal extended key is invalid if is the zero point of Jubjub, or if the corresponding derived from the internal full viewing key as specified in [11] is .
Sapling diversifier derivation
The 88-bit diversifiers for a Sapling extended key are derived from its diversifier key . To prevent the diversifier leaking how many diversified addresses have already been generated for an account, we make the sequence of diversifiers pseudorandom and uncorrelated to that of any other account. In order to reach the maximum possible diversifier range without running into repetitions due to the birthday bound, we use FF1-AES256 as a Pseudo-Random Permutation as follows:
Let be the index of the desired diversifier, in the range .
d_j = \mathsf{FF1}\text{-}\mathsf{AES256.Encrypt}(\mathsf{dk}, \texttt{“”}, \mathsf{I2LEBSP}_{88}(j)).
A valid diversifier is one for which . For a given , approximately half of the possible values of yield valid diversifiers.
The default diversifier for a Sapling extended key is defined to be , where is the least nonnegative integer yielding a valid diversifier.
Specification: Orchard key derivation
The derivation mechanism for Sapling addresses specified above incurs significant complexity to support non-hardened derivation. In the several years since Sapling was deployed, we have seen no use cases for non-hardened derivation appear. With that in mind, we only support hardened key derivation for Orchard.
Orchard extended keys
We represent an Orchard extended spending key as where is the normal Orchard spending key (opaque 32 bytes), and is the chain code.
Orchard master key generation
Let be a seed byte sequence of a chosen length, which MUST be at least 32 and at most 252 bytes.
Calculate I = \mathsf{BLAKE2b}\text{-}\mathsf{512}(\texttt{“ZcashIP32Orchard”}, S).
Split into two 32-byte sequences, and .
Use as the master spending key .
Use as the master chain code .
Return as the master extended spending key .
Orchard child key derivation
Check whether (whether the child is a hardened key).
If so (hardened child): let I = \mathsf{PRF^{expand}}(\mathsf{c}_{par}, [\texttt{0x81}]\,||\,\mathsf{sk}_{par}\,||\,\mathsf{I2LEOSP}_{32}(i)).
If not (normal child): return failure.
Split into two 32-byte sequences, and .
Use as the child spending key .
Use as the child chain code .
Note that the resulting child spending key may produce an invalid external FVK, as specified in [12], with small probability. The corresponding internal FVK derived as specified in the next section may also be invalid with small probability.
Orchard internal key derivation
As in the case of Sapling, for a given external address, we want to produce another address for use by wallets for internal operations such as change and auto-shielding. That is, for any external full viewing key we need to be able to derive a single internal full viewing key that has viewing authority for just internal transfers. We also need to be able to derive the corresponding internal spending key if we have the external spending key.
Let be the spend authorizing key if available, and let be the corresponding external full viewing key, obtained as specified in [12].
Define as follows:
Let .
Let .
Return .
The result of applying to the external full viewing key is the internal full viewing key. The corresponding expanded internal spending key is ,
Unlike Sapling internal key derivation, we do not base this internal key derivation procedure on non-hardened derivation, which is not defined for Orchard. We can obtain the desired separation of viewing authority by modifying only the field relative to the external full viewing key, which results in different , and fields being derived, as specified in [12] and shown in the following diagram:
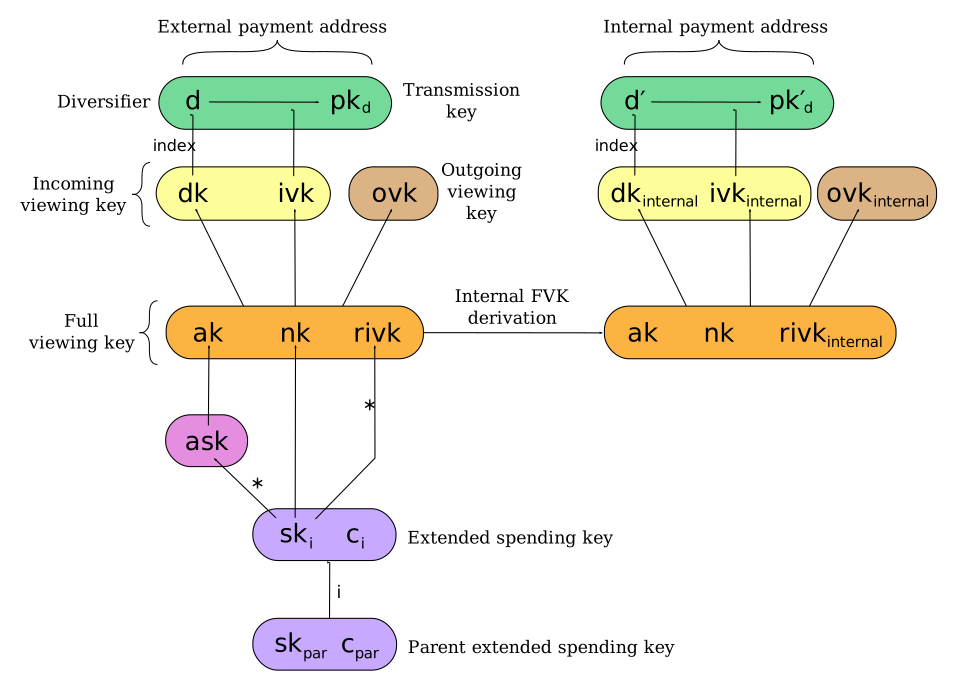
Diagram of Orchard internal key derivation, also showing derivation from the parent extended spending key
This method of deriving internal keys is applied to external keys that are children of the Account level. It was implemented in zcashd as part of support for ZIP 316 [8].
Note that the resulting FVK may be invalid, as specified in [12].
Orchard diversifier derivation
As with Sapling, we define a mechanism for deterministically deriving a sequence of diversifiers, without leaking how many diversified addresses have already been generated for an account. Unlike Sapling, we do so by deriving a diversifier key directly from the full viewing key, instead of as part of the extended spending key. This means that the full viewing key provides the capability to determine the position of a diversifier within the sequence, which matches the capabilities of a Sapling extended full viewing key but simplifies the key structure.
Given an Orchard extended spending key :
Let be the Orchard full viewing key for .
Let and let .
\mathsf{dk}_i = \mathsf{truncate}_{32}(\mathsf{PRF^{expand}}(K, [\texttt{0x82}]\,||\,\mathsf{LEBS2OSP}_{512}(B))).
Let be the index of the desired diversifier, in the range .
d_{i,j} = \mathsf{FF1}\text{-}\mathsf{AES256.Encrypt}(\mathsf{dk}_i, \texttt{“”}, \mathsf{I2LEBSP}_{88}(j)).
Note that unlike Sapling, all Orchard diversifiers are valid, and thus all possible values of yield valid diversifiers.
The default diversifier for is defined to be
Specification: Wallet usage
Existing Zcash-supporting HD wallets all use BIP 44 [5] to organize their derived keys. In order to more easily mesh with existing user experiences, we broadly follow BIP 44's design here. However, we have altered the design where it makes sense to leverage features of shielded addresses.
Key path levels
Sapling and Orchard key paths have the following three path levels at the top, all of which use hardened derivation:
: a constant set to (or \texttt{0x80000020}) following the BIP 43 recommendation. It indicates that the subtree of this node is used according to this specification.
: a constant identifying the cryptocurrency that this subtree's keys are used with. For compatibility with existing BIP 44 implementations, we use the same constants as defined in SLIP 44 [6]. Note that in keeping with that document, all cryptocurrency testnets share index .
: numbered from index in sequentially increasing manner. Defined as in BIP 44 [5].
Unlike BIP 44, none of the shielded key paths have a path level. The use of change addresses in Bitcoin is a (failed) attempt to increase the difficulty of tracking users on the transaction graph, by segregating external and internal address usage. Shielded addresses are never publicly visible in transactions, which means that sending change back to the originating address is indistinguishable from using a change address.
Sapling key path
Sapling provides a mechanism to allow the efficient creation of diversified payment addresses with the same spending authority. A group of such addresses shares the same full viewing key and incoming viewing key, and so creating as many unlinkable addresses as needed does not increase the cost of scanning the block chain for relevant transactions.
The above key path levels include an account identifier, which in all user interfaces is represented as a "bucket of funds" under the control of a single spending authority. Therefore, wallets implementing Sapling ZIP 32 derivation MUST support the following path for any account in range :
.
Furthermore, wallets MUST support generating the default payment address (corresponding to the default diversifier as defined above) for any account they support. They MAY also support generating a stream of payment addresses for a given account, if they wish to maintain the user experience of giving a unique address to each recipient.
Note that a given account can have a maximum of approximately payment addresses, because each diversifier has around a 50% chance of being invalid.
If in certain circumstances a wallet needs to derive independent spend authorities within a single account, they MAY additionally support a non-hardened path level as in [5]:
.
zcashd version 4.6.0 and later uses this to derive "legacy" Sapling addresses from a mnemonic seed phrase under account , using hardened derivation for .
Orchard key path
Orchard supports diversified addresses with the same spending authority (like Sapling). A group of such addresses shares the same full viewing key and incoming viewing key, and so creating as many unlinkable addresses as needed does not increase the cost of scanning the block chain for relevant transactions.
The above key path levels include an account identifier, which in all user interfaces is represented as a "bucket of funds" under the control of a single spending authority. Therefore, wallets implementing Orchard ZIP 32 derivation MUST support the following path for any account in range :
.
Furthermore, wallets MUST support generating the default payment address (corresponding to the default diversifier for Orchard) for any account they support. They MAY also support generating a stream of diversified payment addresses for a given account, if they wish to enable users to give a unique address to each recipient.
Note that a given account can have a maximum of payment addresses (unlike Sapling, all Orchard diversifiers are valid).
Account discovery
A wallet that imports a master seed from an external source SHOULD attempt to discover accounts in the following manner.
Let be the subset of corresponding to master keys for address types that this wallet supports.
For each account index starting from :
For :
Derive the external full viewing key of the account at path .
Scan for transactions sending to this account using the algorithm in [13].
If no transactions are found for either Sapling or Orchard at a given account index, break from the loop over .
If the wallet supports Sapling addresses, then for each address index starting from :
Derive the external full viewing key of the Sapling address at path .
Scan for transactions sending to this address using the algorithm in [13].
If no transactions are found for a range of (Legacy address gap limit) consecutive addresses, break from the loop over .
(The loop over finds legacy Sapling addresses generated by zcashd.)
This algorithm is successful because wallets SHOULD disallow creation of new accounts if the previous one has no transaction history, as described in Key path levels above.
Please note that the algorithm works with the transaction history, not account balances, so you can have an account with zero balance and the algorithm will still continue with discovery.
Legacy address gap limit
The RECOMMENDED address gap limit for legacy Sapling addresses is 20. If a wallet hits this number of unused addresses in a row, it expects there to be no used addresses beyond this point and SHOULD stop searching the legacy Sapling address chain. We scan just the external chains, because internal chains receive only coins that come from the associated external chains.
Wallet software should warn when the user is trying to exceed the gap limit on an external chain by generating a new address.
Specification: Fingerprints and Tags
Sapling Full Viewing Key Fingerprints and Tags
A "Sapling full viewing key fingerprint" of a full viewing key with raw encoding (as specified in [19]) is given by:
\mathsf{BLAKE2b}\text{-}\mathsf{256}(\texttt{“ZcashSaplingFVFP”}, \mathit{FVK}).
It MAY be used to uniquely identify a particular Sapling full viewing key.
A "Sapling full viewing key tag" is the first 4 bytes of the corresponding Sapling full viewing key fingerprint. It is intended for optimizing performance of key lookups, and MUST NOT be assumed to uniquely identify a particular key.
Orchard Full Viewing Key Fingerprints and Tags
An "Orchard full viewing key fingerprint" of a full viewing key with raw encoding (as specified in [21]) is given by:
\mathsf{BLAKE2b}\text{-}\mathsf{256}(\texttt{“ZcashOrchardFVFP”}, \mathit{FVK}).
It MAY be used to uniquely identify a particular Orchard full viewing key.
An "Orchard full viewing key tag" is the first 4 bytes of the corresponding Orchard full viewing key fingerprint. It is intended for optimizing performance of key lookups, and MUST NOT be assumed to uniquely identify a particular key.
Seed Fingerprints
A "seed fingerprint" for the master seed of a hierarchical deterministic wallet is given by:
\mathsf{BLAKE2b}\text{-}\mathsf{256}(\texttt{“Zcash_HD_Seed_FP”},.
It MAY be used to uniquely identify a particular hierarchical deterministic wallet.
No corresponding short tag is defined.
Note: a previous version of this specification did not have the length byte prefixing the seed. The current specification reflects the implementation in zcashd.
Specification: Key Encodings
The following encodings are analogous to the xprv and xpub encodings defined in BIP 32 for transparent keys and addresses. Each key type has a raw representation and a Bech32 [7] encoding.
Sapling extended spending keys
A Sapling extended spending key , at depth , with parent full viewing key tag and child number , is represented as a byte sequence:
.
For the master extended spending key, is , is 4 zero bytes, and is .
When encoded as Bech32, the Human-Readable Part is secret-extended-key-main for the production network, or secret-extended-key-test for the test network.
Sapling extended full viewing keys
A Sapling extended full viewing key , at depth , with parent full viewing key tag and child number , is represented as a byte sequence:
.
For the master extended full viewing key, is , is 4 zero bytes, and is .
When encoded as Bech32, the Human-Readable Part is zxviews for the production network, or zxviewtestsapling for the test network.
Orchard extended spending keys
An Orchard extended spending key , at depth , with parent full viewing key tag and child number , is represented as a byte sequence:
.
For the master extended spending key, is , is 4 zero bytes, and is .
When encoded as Bech32, the Human-Readable Part is secret-orchard-extsk-main for Mainnet, or secret-orchard-extsk-test for Testnet.
We define this encoding for completeness, however given that it includes the capability to derive child spending keys, we expect that most wallets will only expose the regular Orchard spending key encoding to users [22].
Values reserved due to previous specification for Sprout
The following values were previously used in the specification of hierarchical derivation for Sprout, and therefore SHOULD NOT be used in future Zcash-related specifications:
the personalization \texttt{“ZcashIP32_Sprout”}, formerly specified for derivation of the master key of the Sprout tree;
the personalization \texttt{“Zcash_Sprout_AFP”}, formerly specified for generation of Sprout address fingerprints;
the prefix \texttt{0x80}, formerly specified for Sprout child key derivation;
the Bech32 Human-Readable Parts zxsprout and zxtestsprout, formerly specified for Sprout extended spending keys on Mainnet and Testnet respectively.
Test Vectors
TBC